What Makes a Computer Network Work?
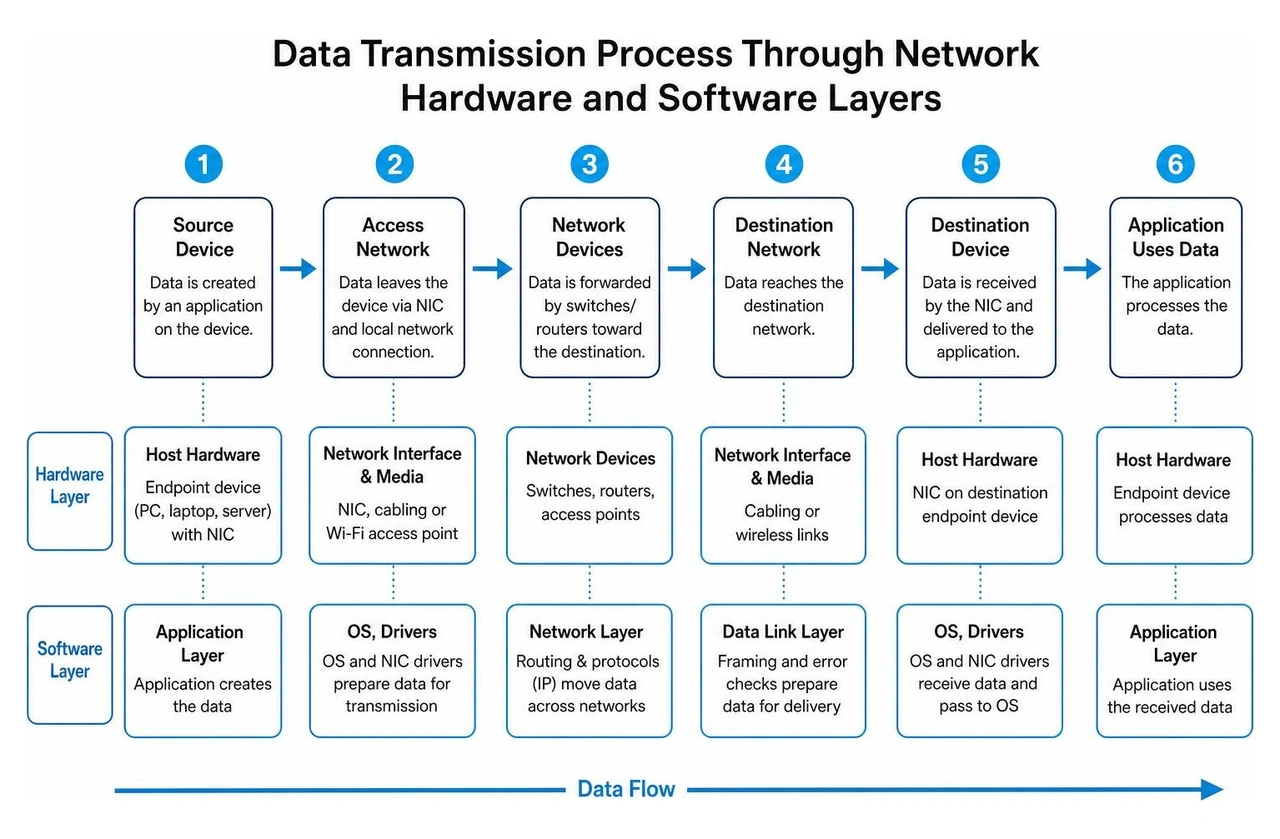
A computer network needs hardware to connect devices and software to make communication possible. Physical equipment like cables, Wi-Fi access points, and network devices work alongside a network interface controller to transmit data between machines. Operating systems, drivers, and protocols such as TCP/IP direct how those devices send, receive, and interpret every packet, while security software and firewalls govern traffic rules.
Both elements are indispensable: high-speed switches cannot overcome a misconfigured subnet, and optimized software cannot fix a damaged cable. Properly managing the hardware and software components of computer network systems requires balanced oversight. Next Level Technologies' technically experienced, cybersecurity-trained teams help organizations maintain this balance from our main location in Columbus, Ohio, and second location in Charleston, WV. For a broader look at foundational topologies and devices, explore our basic computer hardware networking guide.

Understanding the Hardware and Software Components of Computer Network Systems
At its core, a computer network exists to accomplish one goal: move digital information from one endpoint to another accurately, quickly, and securely. To make this happen, physical equipment and programmed instructions must collaborate seamlessly. If we picture a modern shipping company, the networking hardware consists of the roads, trucks, sorting facilities, and shipping docks. The software represents the postal addresses, manifests, traffic rules, tracking systems, and delivery confirmation receipts. Neither works without the other.
Data communication relies on four fundamental pillars: delivery to the correct destination, accuracy of the transmitted payload, timeliness without crippling lag, and minimal jitter (erratic packet delays that ruin voice and video calls). To organize these intricate duties, network architectures adopt a layered modular design. Conceptual frameworks like the Open Systems Interconnection (OSI) reference model separate network operations into seven distinct layers, while practical systems rely heavily on the four-layer TCP/IP stack. As detailed in The TCP/IP Guide - Networking Layers, Models and Architectures, modularity lets engineers upgrade physical cabling or tweak an application protocol independently without overhauling the entire system. Understanding how these layers translate into real-world computer networks is the first step toward building a resilient business infrastructure.
Core Endpoint Hardware and Software Components of Computer Network Setups
Every networked conversation starts and ends at an endpoint host. Endpoints include user workstations, laptops, mobile devices, network-attached storage (NAS), and central network servers.
Network servers require robust internal hardware to sustain dozens or hundreds of simultaneous connections. Unlike standard desktop PCs, enterprise servers feature multi-core processors, substantial error-correcting code (ECC) RAM, redundant power supplies, and storage arrays configured with RAID (Redundant Array of Independent Disks) to ensure continuous operation even if a physical drive fails.
Connecting these endpoints to the wider network infrastructure requires a specialized component known as a network interface controller (NIC). Often built directly into modern motherboards or added via PCIe expansion slots, Ethernet cards support reliable data transfer speeds ranging from 10 Mbps up to 10 Gbps and beyond.
Every physical NIC contains a factory-assigned Media Access Control (MAC) address. This hardware identifier is a 12-digit hexadecimal number (48 bits in length), such as 00:1A:2B:3C:4D:5E. The first half identifies the card manufacturer, while the second half acts as a unique serial number. On the software side, device drivers bridge the gap between the operating system and the NIC hardware, translating high-level data requests into low-level electrical or optical signals.
Once data leaves the NIC, it travels through physical transmission media. The chosen medium dictates bandwidth, distance limits, and vulnerability to electromagnetic interference (EMI).
- Twisted-Pair Copper Cable: The backbone of traditional office local area networks (LANs). Unshielded twisted-pair (UTP) cables, such as Cat5e, Cat6, and Cat6a, use pairs of copper wires twisted together to cancel out cross-talk and external noise. UTP cable runs have a strict physical length limit of 100 meters (roughly 328 feet). Exceeding 100 meters causes signal attenuation, packet loss, and link drops.
- Fiber Optic Cabling: Instead of electrical pulses over copper, fiber optics transmit pulses of light through ultra-pure glass or plastic cores. Fiber optic data transfer rates are 20 to 1,000 times faster than copper cable and outdoor wireless services, reaching speeds over 40 Gbps across dozens of kilometers without signal degradation. By leveraging Wavelength Division Multiplexing (WDM), a single fiber strand can carry multiple communication channels simultaneously on different light frequencies.
- Wireless Radio Frequencies: Non-guided media leverage radio waves to connect wireless adapters inside laptops and smartphones to central wireless access points (WAPs). Modern standards like Wi-Fi 6 and Wi-Fi 7 utilize 2.4 GHz, 5 GHz, and 6 GHz spectrum bands, offering remarkable mobility at the cost of vulnerability to physical obstacles, distance decay, and atmospheric conditions.
For deeper technical study on physical signaling methods, the Department of Computer Science provides exhaustive documentation on signal encoding, multiplexing, and media characteristics.
Key Network Hardware Devices: Connecting and Directing Traffic
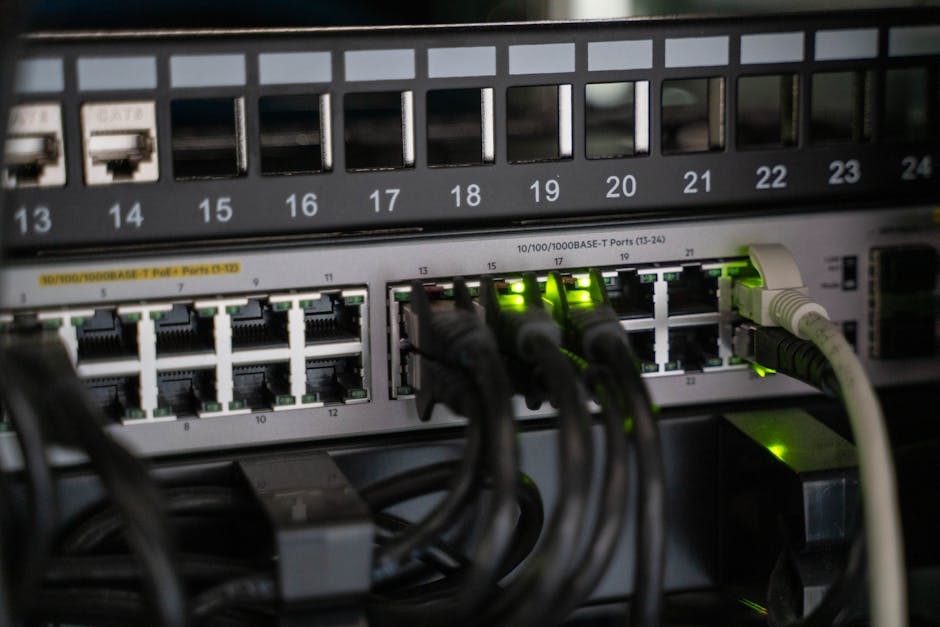
Physical cables and wireless adapters are merely the pathways. To link disparate devices into an organized infrastructure, dedicated network devices must inspect, clean, and forward data across local and wide-area boundaries.
Layer 2 vs Layer 3: Hubs, Switches, Bridges, and Routers
Understanding network traffic management requires distinguishing between data link operations (Layer 2) and internetwork routing (Layer 3). The differences among hubs, switches, bridges, and routers highlight decades of networking innovation:
- Hubs (Layer 1): Legacy devices that act as simple multi-port repeaters. When a packet arrives at one port, the hub blindly broadcasts that electrical signal out to every other connected port. This creates a single large collision domain where devices frequently talk over each other, crippling network efficiency.
- Bridges (Layer 2): Devices designed to break a large network into two distinct physical segments. A bridge acts like a traffic cop at a busy intersection: it reads MAC addresses and only forwards frames across the bridge if the destination device resides on the opposite side, reducing congestion.
- Switches (Layer 2): The modern evolution of the multiport bridge. Switches are commonly configured with 8, 12, 24, or 48 RJ-45 ports. A switch intelligently builds and maintains an internal MAC address table (CAM table) by inspecting incoming frames. When device A sends data to device B, the switch directs the frame exclusively to the specific physical port connected to device B. This isolates traffic, gives each port dedicated bandwidth, and eliminates collision domains entirely.
- Routers (Layer 3): While switches manage traffic inside a single LAN using MAC addresses, routers direct packets between distinct networks using logical IP addresses. Routers maintain complex routing tables and run dynamic protocols (such as OSPF and BGP) to evaluate metrics like hop counts, link speed, and line congestion. They determine the most efficient path for data to travel across interconnected networks or out to the global internet.
Modems, Gateways, and Repeaters
Several other purpose-built hardware appliances perform specialized roles across corporate networks:
- Modems (Modulator-Demodulators): Bridge digital computer networks with analog telecommunication infrastructure. A cable or DSL modem converts the computer's digital binary bits into analog radio-frequency or electrical signals for transmission over public lines, reversing the process for incoming data.
- Gateways: Operate across all layers of the network architecture to connect entirely disparate environments that speak different protocols. A network gateway translates data payloads between different communication standards, such as joining an IP-based corporate network with a legacy mainframe environment.
- Repeaters: Physical layer appliances used when cable runs must exceed standard distance limitations. A repeater receives an incoming electrical or optical signal, cleans away accumulated line noise, amplifies the signal back to its original strength, and retransmits it down the line.
Network Topologies and Architectural Scope
How network components are arranged physically and logically shapes performance, fault tolerance, and implementation cost.
Physical Topologies: Star, Bus, Ring, and Mesh
- Star Topology: The ubiquitous standard for modern enterprise LANs. Every endpoint connects directly to a central switch. If a single workstation cable is damaged, only that machine loses access while the rest of the company continues working uninterrupted. Troubleshooting is straightforward, although the central switch represents a single point of failure if not deployed with hardware redundancy.
- Bus Topology: An older design where all devices connect in a daisy-chain fashion to a single central backbone cable terminated with resistors at each end. While inexpensive and easy to deploy for a few devices, a break anywhere along the primary bus cable breaks the entire network.
- Ring Topology: Devices connect in a continuous circular loop where data travels sequentially from node to node using token-passing mechanisms. A break in the physical ring can disable communication unless dual counter-rotating rings are deployed.
- Mesh Topology: Provides unmatched reliability and fault tolerance. In a fully connected mesh network containing n nodes, the infrastructure requires n(n - 1) / 2 physical links. Because every device maintains dedicated direct connections to every other device, multiple redundant paths exist if any line fails. While cost and cabling complexity make full mesh networks rare for end-user workstations, it remains the standard topology inside carrier-grade data centers and internet backbones.
- Tree (Hierarchical) Topology: Combines star networks into an interconnected hierarchical structure, with access layer switches feeding into distribution switches and a high-speed core backbone.
Network Coverage Areas: PAN, LAN, MAN, and WAN
Networks are categorized by geographic footprint, administration model, and transmission medium:
- Personal Area Network (PAN): Connects personal devices within a range of a few meters, typically using short-range wireless technologies like Bluetooth or Wi-Fi Direct.
- Local Area Network (LAN): Confined to a single room, office suite, building, or school campus. LANs are privately owned, utilize high-speed Ethernet and Wi-Fi, and offer low latency, typically below 2 milliseconds.
- Metropolitan Area Network (MAN): Covers an entire city or large municipal region, frequently linking multiple branch offices, municipal facilities, and regional hospitals using high-capacity dark fiber backbones.
- Wide Area Network (WAN): Spans broad geographic regions, states, nations, or the entire globe. WANs interconnect dispersed LANs across public telecom infrastructure, fiber lines, cellular links, and satellite links. While wired LANs boast sub-2 millisecond latency, satellite-based WAN connections can introduce latencies exceeding 500 milliseconds due to the vast travel distance to orbit.
Essential Networking Software, Protocols, and Operating Systems
Hardware provides the physical foundation, but software dictates the logic of communication. Without standardized operating systems and communication rules, network devices would remain isolated islands of silicon and copper.
The TCP/IP Protocol Suite and Addressing Models
The TCP/IP suite is the universal language of modern networking. It governs how data is packetized, addressed, transmitted, routed, and received:
- TCP (Transmission Control Protocol): A connection-oriented, reliable transport protocol. Before transmitting data, TCP establishes a verified connection using a formal 3-way handshake (SYN, SYN-ACK, ACK). It numbers every packet, manages data flow, tracks acknowledgments, and automatically retransmits lost packets to guarantee complete, error-free delivery (ideal for web pages, file downloads, and email).
- UDP (User Datagram Protocol): A connectionless, lightweight protocol. UDP fires packets toward the recipient without establishing a prior connection or verifying receipt. This lack of overhead makes UDP exceptionally fast, making it the preferred choice for real-time voice (VoIP), video conferencing, and live streaming where a dropped millisecond of audio is preferable to a delayed conversation.
- IPv4 vs. IPv6 Addressing: Every device on a TCP/IP network requires a unique logical address. The legacy IPv4 standard uses 32-bit addresses written in dotted-decimal format (e.g.,
192.168.1.1), yielding just under 4.3 billion unique addresses—a pool completely exhausted by the surge of smartphones, PCs, and IoT appliances. The modern IPv6 standard solves this by using 128-bit hexadecimal addresses, generating 3.4 × 10^38 possible addresses, enough to assign billions of unique addresses to every grain of sand on Earth. - NAT (Network Address Translation): To conserve IPv4 space, local routers use private IP ranges (such as
10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16) internally. NAT enables hundreds of local devices sharing private IP addresses to access the public internet simultaneously behind a single, publicly routable IP address.
Network Operating Systems and Core Services
Specialized Network Operating Systems (NOS), such as Microsoft Windows Server and enterprise Linux distributions (Red Hat, Ubuntu Server), coordinate client-server interactions, enforce security policies, and manage directory permissions. Core services include:
- DHCP (Dynamic Host Configuration Protocol): Automates network setup by leasing IP addresses, subnet masks, default gateways, and DNS settings to devices as they join the network, eliminating manual configuration errors.
- DNS (Domain Name System): Acts as the address book of the internet. When a user types a human-readable domain name into a browser, DNS translates that alphanumeric name into the destination machine's numerical IP address through a hierarchical query chain involving root servers, top-level domain (TLD) servers, and authoritative nameservers.
- Cloud Infrastructure (IaaS, PaaS, SaaS): Modern software architectures often abstract on-premise hardware entirely. Infrastructure as a Service (IaaS) provides virtualized computing and software-defined networks in the cloud; Platform as a Service (PaaS) offers deployment frameworks for developers; and Software as a Service (SaaS) delivers fully managed business applications over the web.
Defending the Perimeter: Security Hardware and Software
A functional network must be a secure network. Effective security requires a multi-layered defense strategy that embeds protections into both hardware appliances and operating software.
Aligning Hardware and Software Components of Computer Network Security
Relying on a single line of defense leaves critical infrastructure vulnerable. Hardware and software safeguards work together across the environment:
- Hardware Security Appliances: Dedicated enterprise firewalls and Unified Threat Management (UTM) devices sit directly at the perimeter between the internal network and the public internet. They perform high-throughput stateful packet inspection, deep packet analysis, hardware-accelerated intrusion prevention (IPS), and content filtering before untrusted traffic ever reaches internal machines.
- Software Protections and Encryption: At the host layer, software-based firewalls, centralized endpoint protection, and managed antivirus guard individual machines against lateral malware movement. Software protocols enforce end-to-end data security: Transport Layer Security (TLS) encrypts web transactions, IPsec secures site-to-site VPN tunnels, and WPA3 encryption shields wireless radio transmissions from eavesdropping.
Network administrators and IT engineers rely on built-in software utilities to diagnose hardware faults, misconfigurations, and performance bottlenecks:
- ping: Sends ICMP Echo Request packets to a target IP or domain to verify basic layer 3 connectivity, measuring round-trip time and packet loss.
- traceroute (or tracert): Maps the complete hop-by-hop path packets take to reach a destination, exposing exactly which intermediate router or ISP link is failing or experiencing severe latency.
- dig (or nslookup): Queries DNS nameservers directly to test name resolution records, verify mail exchanger (MX) entries, and diagnose TTL caching issues.
- netstat: Displays all active network connections, listening ports, and protocol statistics on a local computer.
- iperf: Measures maximum achievable bandwidth across a network link, helping engineers identify duplex mismatches or failing cabling.
Frequently Asked Questions About Network Architecture
What is the main difference between a network hub and a network switch?
A hub operates at Layer 1 and blindly repeats all incoming data packets out to every connected port, creating high collision rates and wasting bandwidth. A switch operates at Layer 2, reading hardware MAC addresses to build an internal port map and directing data frames solely to the intended recipient's port.
Why is DNS considered a critical software component of computer networks?
Without DNS, users would need to memorize complex numerical IP addresses (like 142.250.190.46 for IPv4 or long hexadecimal IPv6 strings) for every website, server, and cloud service. DNS automates this translation instantly behind the scenes, making modern internet navigation and distributed cloud systems practical.
When is a physical repeater necessary instead of adding a new switch?
A repeater is used when you need to extend an unmanaged, point-to-point cable run past standard physical limits (such as the 100-meter threshold for twisted-pair copper) without needing additional local switching, MAC address processing, or port aggregation. However, in modern corporate environments, managed switches are preferred because they provide signal regeneration along with traffic segmentation and VLAN capabilities.
Conclusion
A dependable, high-performance IT infrastructure is never an accident. It is the result of aligning quality hardware components—durable cabling, high-speed NICs, managed switches, and enterprise routers—with robust software protocols, reliable network operating systems, and proactive cybersecurity policies. When any single piece of the chain is neglected, the entire organization risks frustrating downtime, application latency, and dangerous security vulnerabilities.
At Next Level Technologies, our technical team brings extensive cybersecurity training and over two decades of practical experience to every deployment. We help small and mid-sized businesses design, secure, and manage high-availability networks with predictable performance. Whether you need a comprehensive infrastructure audit, proactive monitoring, or turnkey managed IT support, our local specialists are ready to help from our main location in Columbus, Ohio, and our second location in Charleston, WV. Contact us today to ensure your network hardware and software work together seamlessly.